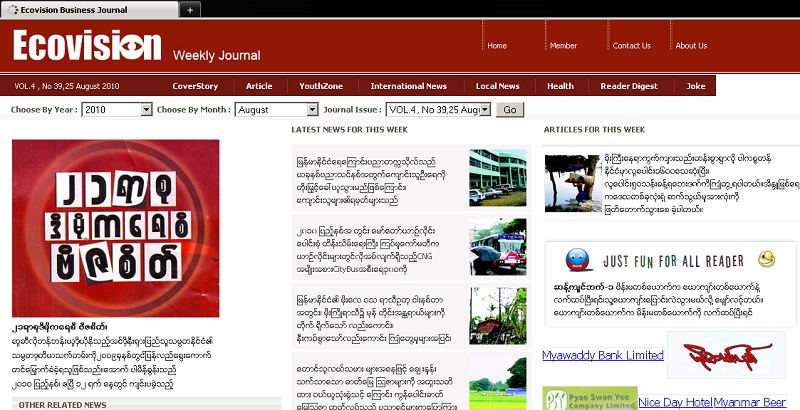
Security Researcher $@T0R! reported another Critical SQL Injection in http://www.ecovisionjournal.com – Weekly Journal
SQL injection is a code injection technique that exploits a security vulnerability occurring in the database layer of an application. The vulnerability is present when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and thereby unexpectedly executed. It is an instance of a more general class of vulnerabilities that can occur whenever one programming or scripting language is embedded inside another.
This is critical and reported to webmaster:
These are some info and screenshots from vul site:
5.0.45-community-nt:[email protected]:ecobase
Tables eco_comment_type,eco_mail_list,eco_month_list,eco_poll_qus,eco_reader_digest, eco_tbl_applicant,eco_tbl_article,eco_tbl_category,eco_tbl_comment,eco_tbl_coverstory, eco_tbl_data,eco_tbl_health,eco_tbl_interview,eco_tbl_issue,eco_tbl_joke,eco_tbl_member, eco_tbl_news,eco_tbl_product,eco_tbl_yzone,eco_vote_ans,eco_year_list
Columns
id,type,NO,name,mail,ID,mName,yID,pno,pTitle,RID,Header,Pic,issue,rate,shortnotes, detaildata,appNo,Name,DOB,NRC,Address,Email,Education,Skill,Experience,CurrentJob, Company,Office,AppliedFor,Shift,CurrentSalary,ExpectedSalary,ContactNo,Photograph, ApplyTo,ID,title,apath,Img,issue,rate,shortnotes,ID,cName,id,comment,type_id, time,Isshow,volume
We hope that your security staff will look into this issue and fix it as soon as possible.