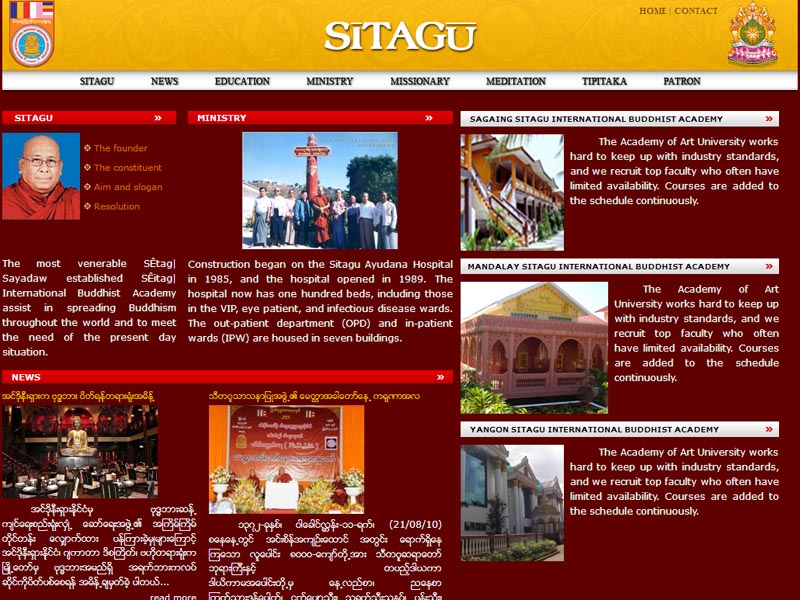
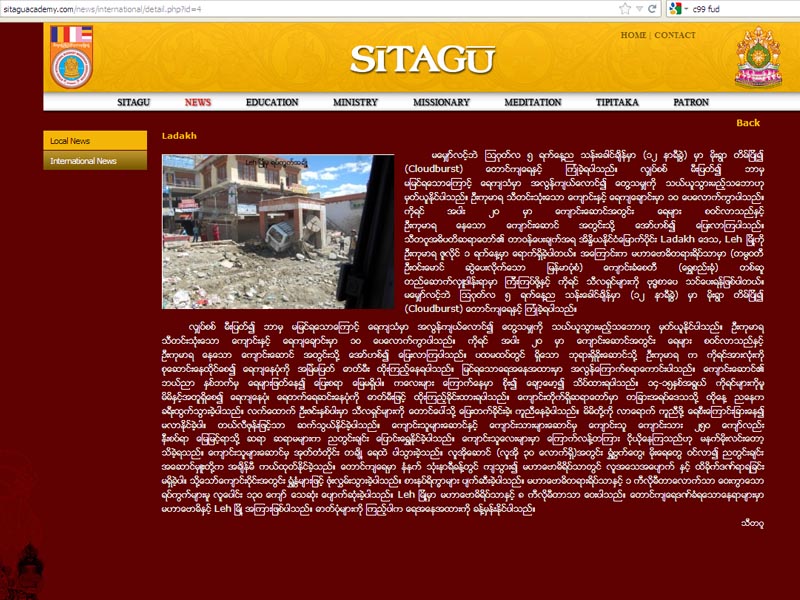
Security researcher Dr@GoN 3y3 reported another Critical SQL injection (vulnerability) on SITAGU :: Sitagu International Buddhist Missionary Centre http://www.sitaguacademy.com/
SQL injection is a code injection technique that exploits a security vulnerability occurring in the database layer of an application. The vulnerability is present when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and thereby unexpectedly executed.
informed to :- webmaster
This is vulnerability is posted at Vulnerabilities Research Page http://www.planetcreator.net/info
Risk Level : Critical , It’s plain text password, some more, attacker can easily upload hacking shell at posting session, There’s no upload file extension filtering too.
Check Additional Information about this vulnerability at http://www.planetcreator.net/info/exploits/id/107/
We hope that your security staff will look into this issue and fix it as soon as possible.