PlanetCreator has reported another critical SQL Injection (vulnerability) on National Library, Ministry of Culture Website http://www.nlm.gov.mm/

SQL injection is a code injection technique that exploits a security vulnerability occurring in the database layer of an application. The vulnerability is present when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and thereby unexpectedly executed.

This vulnerability has been alerted to :- [email protected]
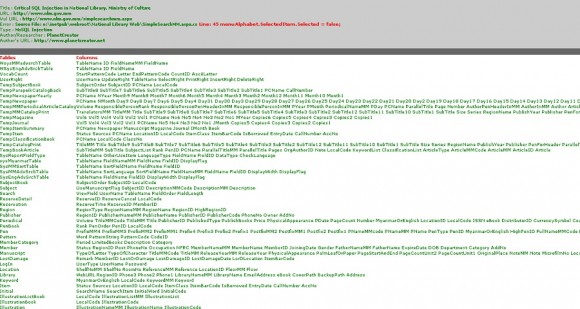
If you want to see detail of this vulnerability Click Here (Note :- Registered Member Only- If you are not PlanetCreator.Net Member Sign up Here)

We hope that your security staff will look into this issue and fix it as soon as possible.

Explore More

Critical Blind SQL Injection (vulnerability) in The Best Myanmar Website (burmeseclassic.com)

PlanetCreator has reported another critical Blind SQL Injection (vulnerability) on http://www.burmeseclassic.com/ This vulnerability has been alerted to :- Webmaster of BurmeseClassic Applications: ———— PlanetCreator’s_Universal_Advanced_Internet_Security_T00L System Time: ———— (UTC+08:00) Yangoon, Myanmar

Windows rootkits 101

When administrators and security professionals hear the word rootkit, most think first of a UNIX-based system. Unfortunately, this only leads to a false sense of security for Windows-based systems. The

Hacking

Hacking is an unauthorized access of computers and networks. It is the act of piercing computer systems gaining knowledge of the systems and the learning of how it works. The