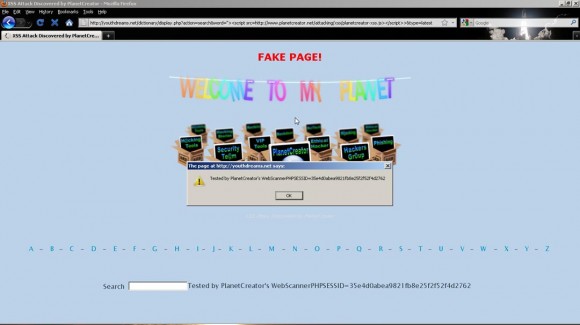
Security Researcher $@T0R! reported another XSS vulnerability in http://www.youthdreams.net

Cross-site scripting (XSS) is a type of computer security vulnerability typically found in web applications that enables malicious attackers to inject client-side script into web pages viewed by other users. An exploited cross-site scripting vulnerability can be used by attackers to bypass access controls such as the same origin policy.

Vul: – http://youthdreams.net

We hope that your security staff will look into this issue and fix it as soon as possible.

Explore More

XSS Stealing Cookies

This method (XSS attacks) is for get the cookies users, so, for get information of users… and then, login into the account of the victim user…u will have to give

fimap v.0.9 released

fimap is a little python tool which can find, prepare, audit, exploit and even google automaticly for local and remote file inclusion bugs in webapps. fimap should be something like

[Tut/Sources] References to poly/meta/permutation

Articles: Polymorphic engines – Trigger – SLAM #4 Code: http://vx.netlux.org/lib/static/vdat/tupoleng.htm Polymorphism ant Intel instruction format – LiTlLe VxW – 29A #7 Code: http://vx.netlux.org/29a/29a-7/Articles/29A-7.027 Guide to improving Polymorphic Engines – Rogue